“The question is never whether a flagged individual has ever been screened. The question is whether they were screened today and whether you can prove it.”
It’s a Tuesday morning at a defense contractor’s manufacturing facility. A technician arrives at the front desk, presents a paper ID, and signs in on a clipboard. The receptionist is managing three other things. The name is unfamiliar. The technician is waved through.
Twelve weeks later, during a routine CMMC audit, the compliance team discovers the visitor had been flagged on an internal deny list following an incident at a partner facility, two months before this visit. The breach went undetected because no deny list screening was run at check-in. The technician had site access for six hours.
The cost: a delayed contract renewal, a mandatory security review, and six months of remediation work. This is what reactive security looks like. This is why enterprises have moved to automated watchlist screening.
What Is Visitor Screening?
Visitor screening is checking who a person is, and whether they should be let in, before they reach the floor. It covers three checks: confirming identity from a government ID, matching the person against the lists your organization keeps and the lists governments publish, and getting the host's approval. When a check finds a match, the check-in is held until security decides.
Why Manual Screening Gets Wrong
Most enterprise facilities still rely on some version of manual sign-in: a front-desk workflow in which a staff member checks a government-issued ID, records a name, and issues a badge. It looks like security. It isn’t.
Front desk staff cannot realistically cross-reference a visitor’s name against multiple watchlists in real time. They’re managing phone calls, package deliveries, and employee requests simultaneously. A brief name check against a clipboard is the operational reality for most facilities, and it’s nowhere near sufficient for regulated environments.
Rotating contractors compounds the problem significantly. A contractor flagged after an incident at Location A has no footprint in Location B’s paper log. There’s no shared record, no automated alert, and no mechanism to catch a returning individual whose clearance has been revoked. At multi-site enterprises, this is a daily exposure.
When auditors request visitor access records for ITAR compliance reviews, SOC 2 Type II assessments, or CMMC evaluations, paper logs and disconnected spreadsheets consistently fail to satisfy documentation requirements. There’s no timestamped chain of custody, no identity verification record, and no evidence of systematic screening. The audit finding writes itself.
Practical note: the organizations that fail physical access reviews are rarely the ones that lack controls entirely. They are the ones who have controls but cannot prove them – because the process was manual and the record is incomplete.
How Automated Watchlist Screening Works
Automated watchlist screening removes the manual bottleneck entirely. The flow from arrival to alert operates in seconds:
- A visitor or contractor arrives and initiates check-in at a lobby kiosk powered by lobby security software. Pre-registered visitors can use a QR code to streamline the process.
- Photo ID is captured, and identity is verified. A government-issued ID is scanned and cross-referenced with the visitor’s declared identity, automatically creating a timestamped identity record.
- Facial recognition cross-references the captured photo against stored watchlist profiles, catching individuals using name changes, aliases, or altered documentation that name-only screening would miss entirely.
- The system simultaneously checks against internal deny lists, sex offender registries, custom contractor blocklists, and government watchlists in a single, automated query with no manual lookup required.
- A match triggers instant alerts to the security team via Slack, Microsoft Teams, SMS, or email before the visitor reaches the floor. The visitor is held at the lobby while security responds.
- Every check-in – successful, flagged, or denied – is logged automatically with a tamper-evident timestamp, creating a complete audit trail across every location in real time.
The facial recognition check-in layer is what separates automated screening from a name-match system. It anchors identity verification to a biometric record, not to what the visitor chose to type, closing the alias and nickname gap that manual processes can never close.
Practical note: alert routing is configurable per location and per risk level. R&D facilities and controlled manufacturing areas can be set to require security team acknowledgment before any access is granted. Corporate lobbies can use a lighter workflow while maintaining the same audit trail.

Screening Visitors Against Sanctions and Denied-Party Lists
Your own watchlist covers people you already know about: former employees, banned contractors, individuals involved in past incidents. Government sanctions and denied-party lists cover people your organization has never met, such as individuals and companies on the US Treasury's OFAC sanctions lists. At defense, aerospace and other export-controlled sites, the stakes are specific: showing controlled technology to the wrong person can count as an export under ITAR and EAR rules, even when nothing physical leaves the building.
One check at the kiosk can cover:
- The watchlists your organization maintains
- Government sanctions lists, such as OFAC
- Criminal databases
- Sex offender registries
Visitly runs these checks natively, or through the screening platform your compliance team already uses, such as Visual Compliance or First Advantage. When a visitor matches, the check-in is held, security is notified, and an officer decides whether to approve or deny entry. Every result, clear or flagged, is logged with a timestamp, so the screening record is ready when an auditor asks for it.
Screening does not have to wait for the front desk. With PreScreen, Visitly screens a guest when the host invites them, before the invitation goes out. Security knows about a match ahead of time, and the visit can be sorted out before anyone is turned away at the door.
Practical note: if your trade compliance team already screens customers and suppliers in a dedicated platform, visitors can be checked against the same lists. Trade compliance and site security then work from one source instead of two.

Why Contractors Are the Highest-Risk Gap
- Contractors are the highest-volume, most underscreened population in enterprise facilities. Unlike employees, they bypass the standard onboarding and vetting pipeline. Many arrive via third-party staffing firms, with varying clearance levels and access requirements that can change at any time, and that the host facility may never directly verify.
- In a multi-vendor environment, a mid-size manufacturing plant may see 40 to 60 contractors per day across maintenance, technology, logistics, and construction. Each carries different access rights, and some may have had clearances revoked after an incident that the host facility has no visibility into.
- One-time screening at onboarding is not sufficient. Contractor status changes, clearances get revoked, and individuals get flagged at partner sites. Effective contractor management means screening at every visit, not just the first one, so that status changes are caught before site access is granted.
- A contractor management system with automated check-in ties NDA signing and compliance document acknowledgment directly to the visitor management workflow. Contractors cannot proceed to the floor without digitally confirming the relevant agreements for that visit. That acknowledgment is logged, timestamped, and attached to their visitor record, producing the documentation chain that ITAR compliance and CMMC auditors require.
The question is not whether a contractor was screened at hire. The question is whether they were screened today and whether you can prove it to an auditor six months from now.
Compliance Frameworks That Require Visitor and Contractor Screening Documentation
Security professionals often treat the visitor management system as an operational concern. Auditors treat it as a control. Each of the major regulatory frameworks governing defense, healthcare, and technology enterprises has specific documentation requirements for physical access control, and manual screening processes consistently fail to meet them.
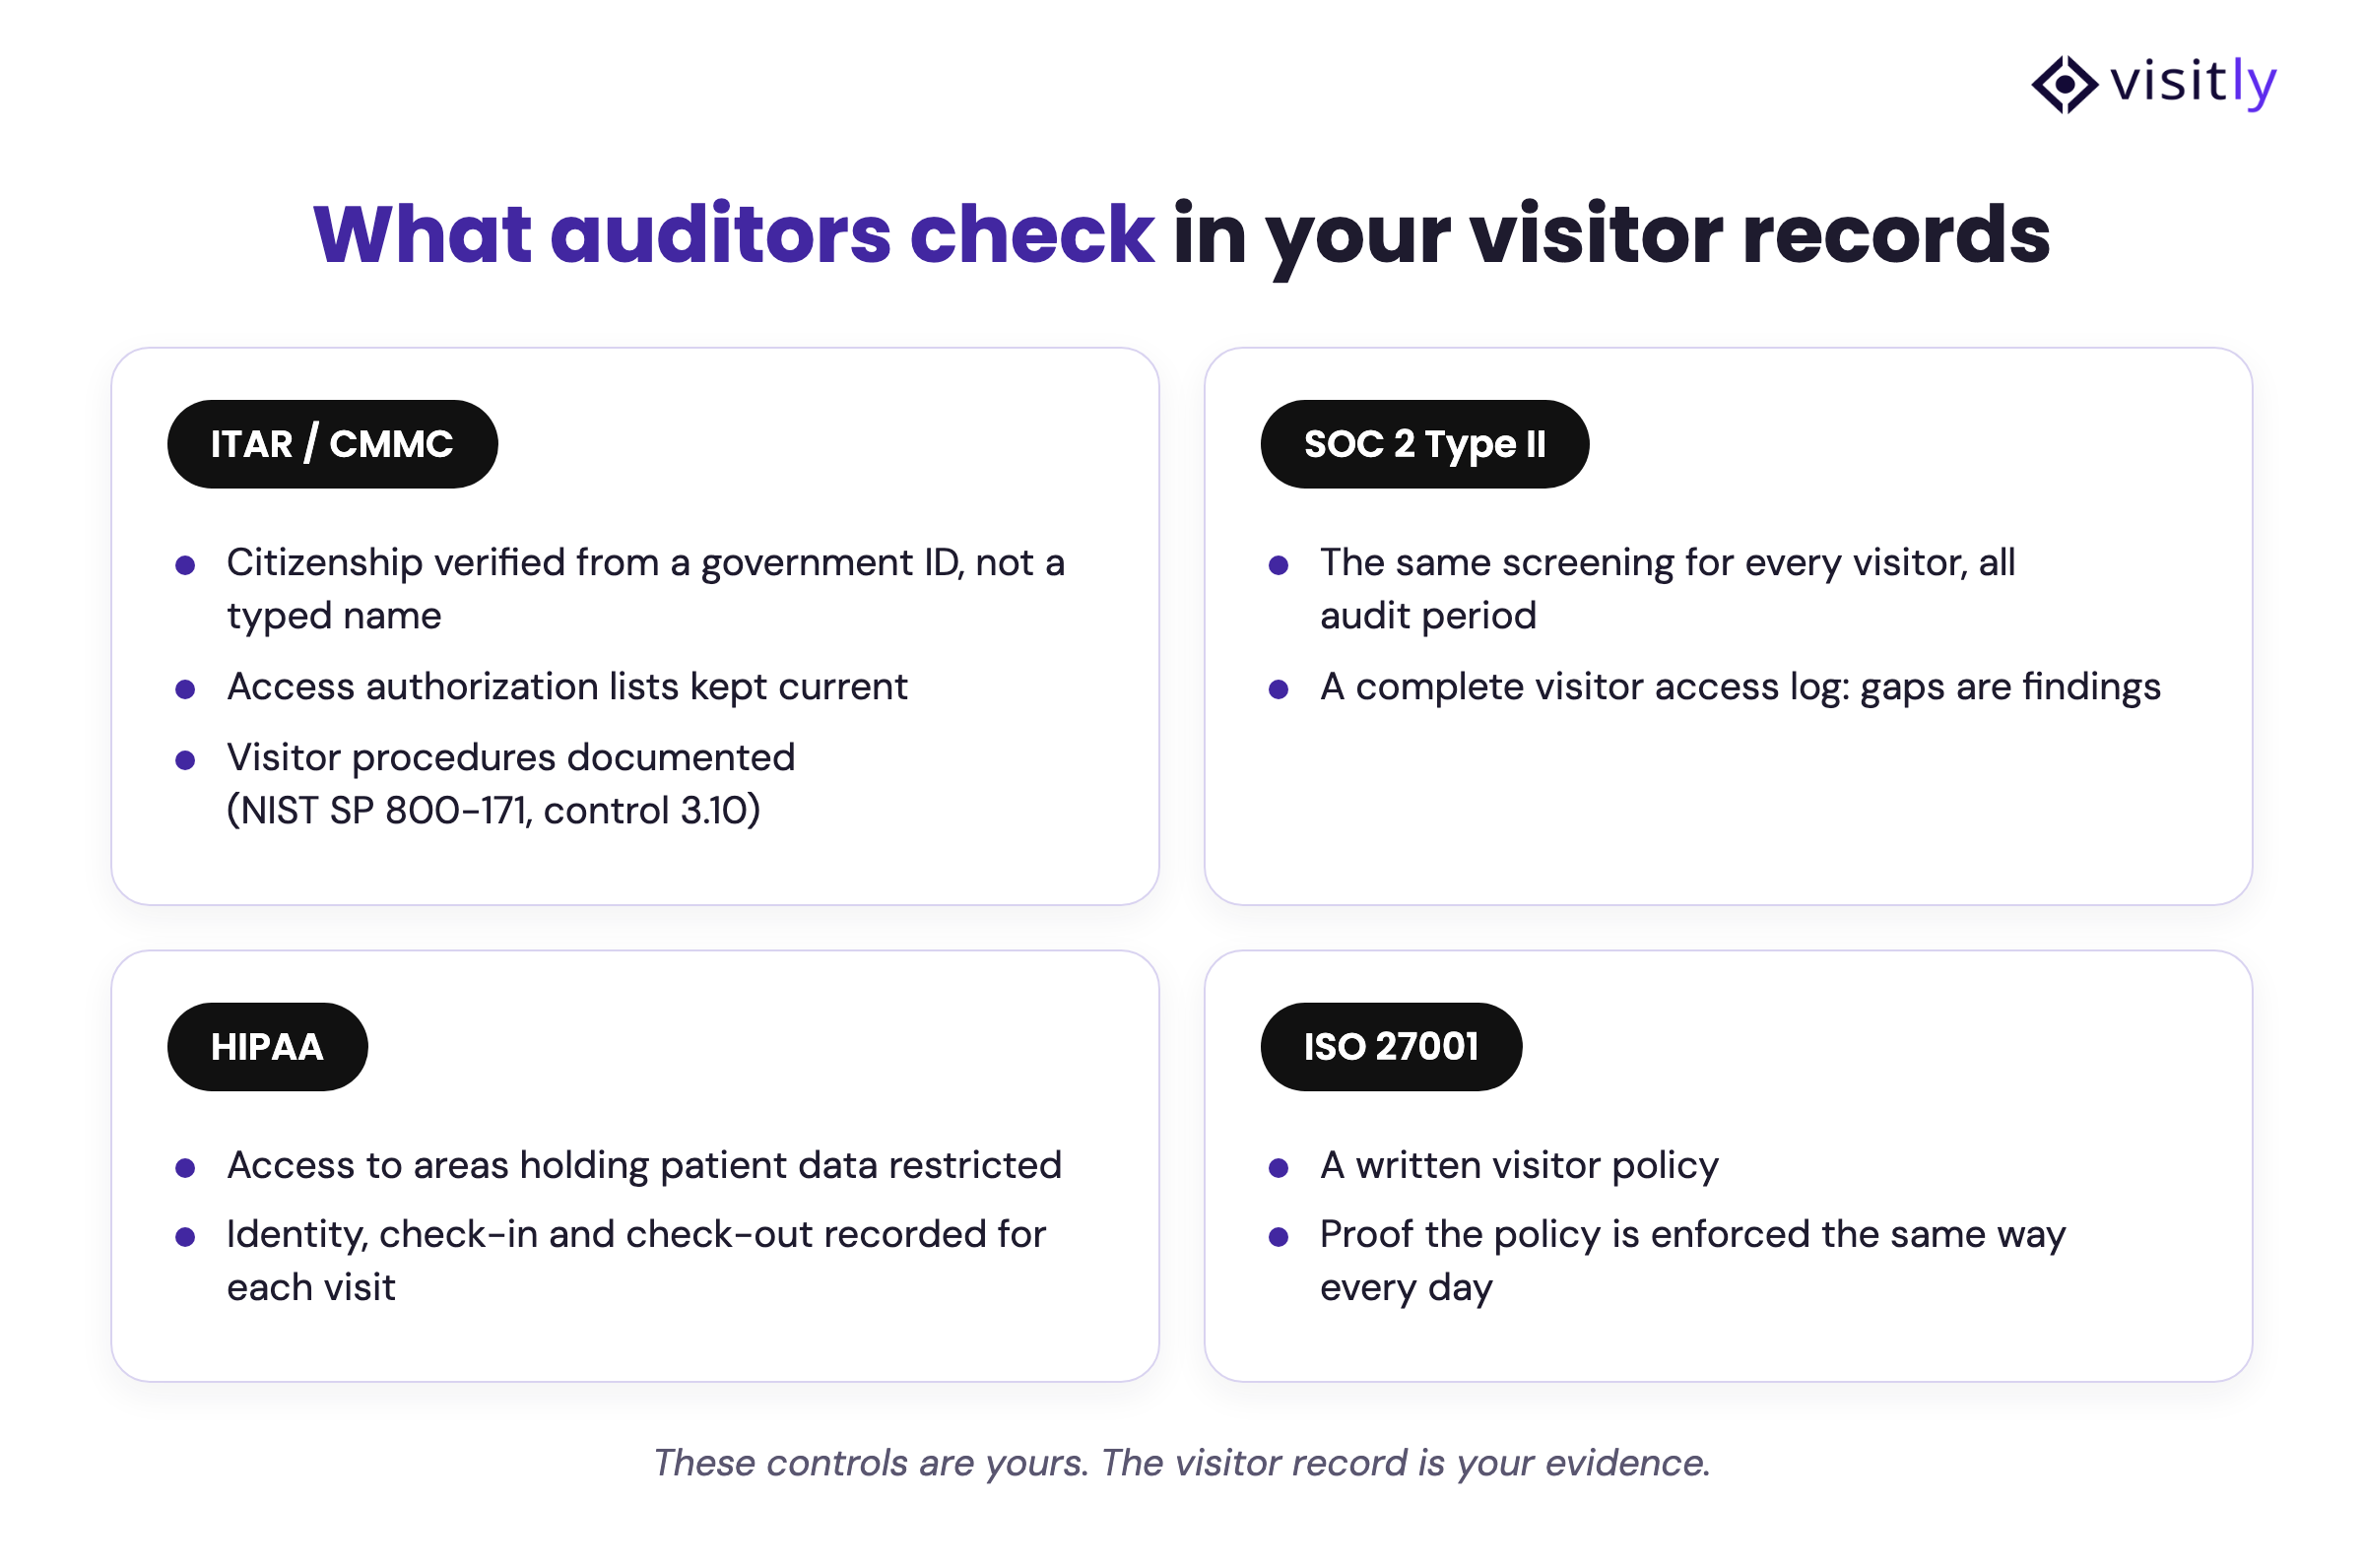
- ITAR / CMMC
ITAR requires that defense manufacturers restrict access to controlled technical data and manufacturing areas to U.S. individuals or specifically authorized foreign nationals. Verifying that status requires verifying a government document, not a name the visitor typed.
CMMC Level 2 maps directly to NIST SP 800-171 control family 3.10: organizations must maintain access authorization lists, verify identity before granting entry, and document visitor management procedures.
Third-party assessment organizations will ask not just whether identity was checked, but how. A manual log is difficult to defend in response to that question.
- SOC 2 Type II
Visitor access logs are evaluated as part of physical security controls in a SOC 2 Type II audit. Auditors look for systematic, consistent screening throughout the audit period, not ad hoc front-desk decisions.
Gaps in the log are findings. Visitor management software with automated logging produces structured, searchable evidence that satisfies this requirement by default.
- HIPAA
Facilities housing protected health information must enforce and document access restrictions as a required physical safeguard. Visitor screening is not optional under HIPAA. Unverified access to PHI areas creates direct liability.
A system that captures identity, logs check-in and check-out, and generates a timestamped access record satisfies this requirement in a way that a handwritten visitor log does not.
- ISO 27001
ISO 27001 requires documented visitor policies and evidence that those policies are enforced consistently. Certification audits evaluate whether visitor management controls are operational, not just written down. Automated screening provides the enforcement record that auditors are looking for.
An audit is not the time to discover your screening process was manual and inconsistent. By then, the finding is already written.
What Enterprise Deployment Looks Like
The most common concern security leaders raise about deploying new physical security platforms is operational disruption, particularly across multiple locations with different workflows and risk profiles. The deployment model for automated watchlist screening addresses these issues directly, without compromising physical security compliance.
Centralized watchlist management means that one update propagates instantly across all locations. A contractor flagged at your Austin facility is screened out at your Singapore site before the next check-in attempt. There is no delay, no manual distribution, and no location that runs on a stale list.
Per-location configuration allows stricter screening thresholds for R&D labs, server rooms, and controlled manufacturing zones while maintaining a lighter workflow for corporate lobbies and general visitor areas. Every location runs on the same platform and feeds the same audit trail.
Native integrations with Okta, Azure Active Directory, and existing physical access control systems connect the platform to the identity infrastructure already in place. SSO and SCIM provisioning work from day one. No rip-and-replace required.
A real-time dashboard gives security leadership visibility into who is on-site, who was flagged, and who was denied across all locations in a single view. A multi-site rollout takes one week to one month, depending on how prepared your sites are.
Book a Security Demo
If your team is evaluating enterprise watchlist screening, a Visitly security consultation takes 30 minutes and focuses on your specific compliance requirements, facility footprint, and existing security stack.
Connect with Visitly for more information about automated watchlists that screen visitors & contractors in real time.

FAQs
What is automated watchlist screening?
Automated watchlist screening checks every visitor and contractor against your deny lists at check-in, before a badge prints. The check runs on the identity captured at the kiosk, and a match holds the check-in and alerts security. Large enterprises manage the list centrally, so a person flagged at one location is stopped at every other location.
What is visitor screening?
Visitor screening is checking each person before entry: confirming identity, checking them against your watchlists and government sanctions lists, and getting host approval. Visitly runs these checks at pre-registration and again at check-in, holds the check-in on a match and alerts security, so the decision is made before a badge prints.
Does watchlist screening need to happen at every visit, or only at onboarding?
Every visit. A contractor's status can change between onboarding and the next arrival, for example after an incident at another location or when a contract ends. A one-time check at onboarding misses that change. Screening at each check-in catches it before access is granted, and it leaves a dated record that the check ran that day.
Which compliance frameworks expect visitor screening records?
Several frameworks expect records of who entered and how access was controlled. CMMC Level 1 covers escorting visitors, monitoring their activity and keeping physical access logs. ITAR restricts foreign-person access to controlled technical data. SOC 2 and ISO 27001 audits review physical access controls, visitors included. Your compliance lead or counsel decides what each framework requires at your locations.
How long does it take to deploy watchlist screening across multiple locations?
Plan on one week to one month for a multi-site rollout, depending on how prepared your sites are. On Visitly, a basic setup can be done in under an hour, and integrations such as single sign-on, SCIM, access control and HR systems take a couple of days. Visitly includes watchlist and photo ID screening at $2,000 per location per year.
Is watchlist screening the same as denied-party screening?
No. A watchlist holds the names your organization decides to block or flag, such as former employees or banned contractors. Denied-party screening checks visitors against government sanctions and restricted-party lists, such as OFAC. Visitly does both: it screens against the watchlists you configure, and against sanctions lists directly or through an integration with the screening platform you choose.