CMMC visitor logs and escort records that support your Level 2 program.
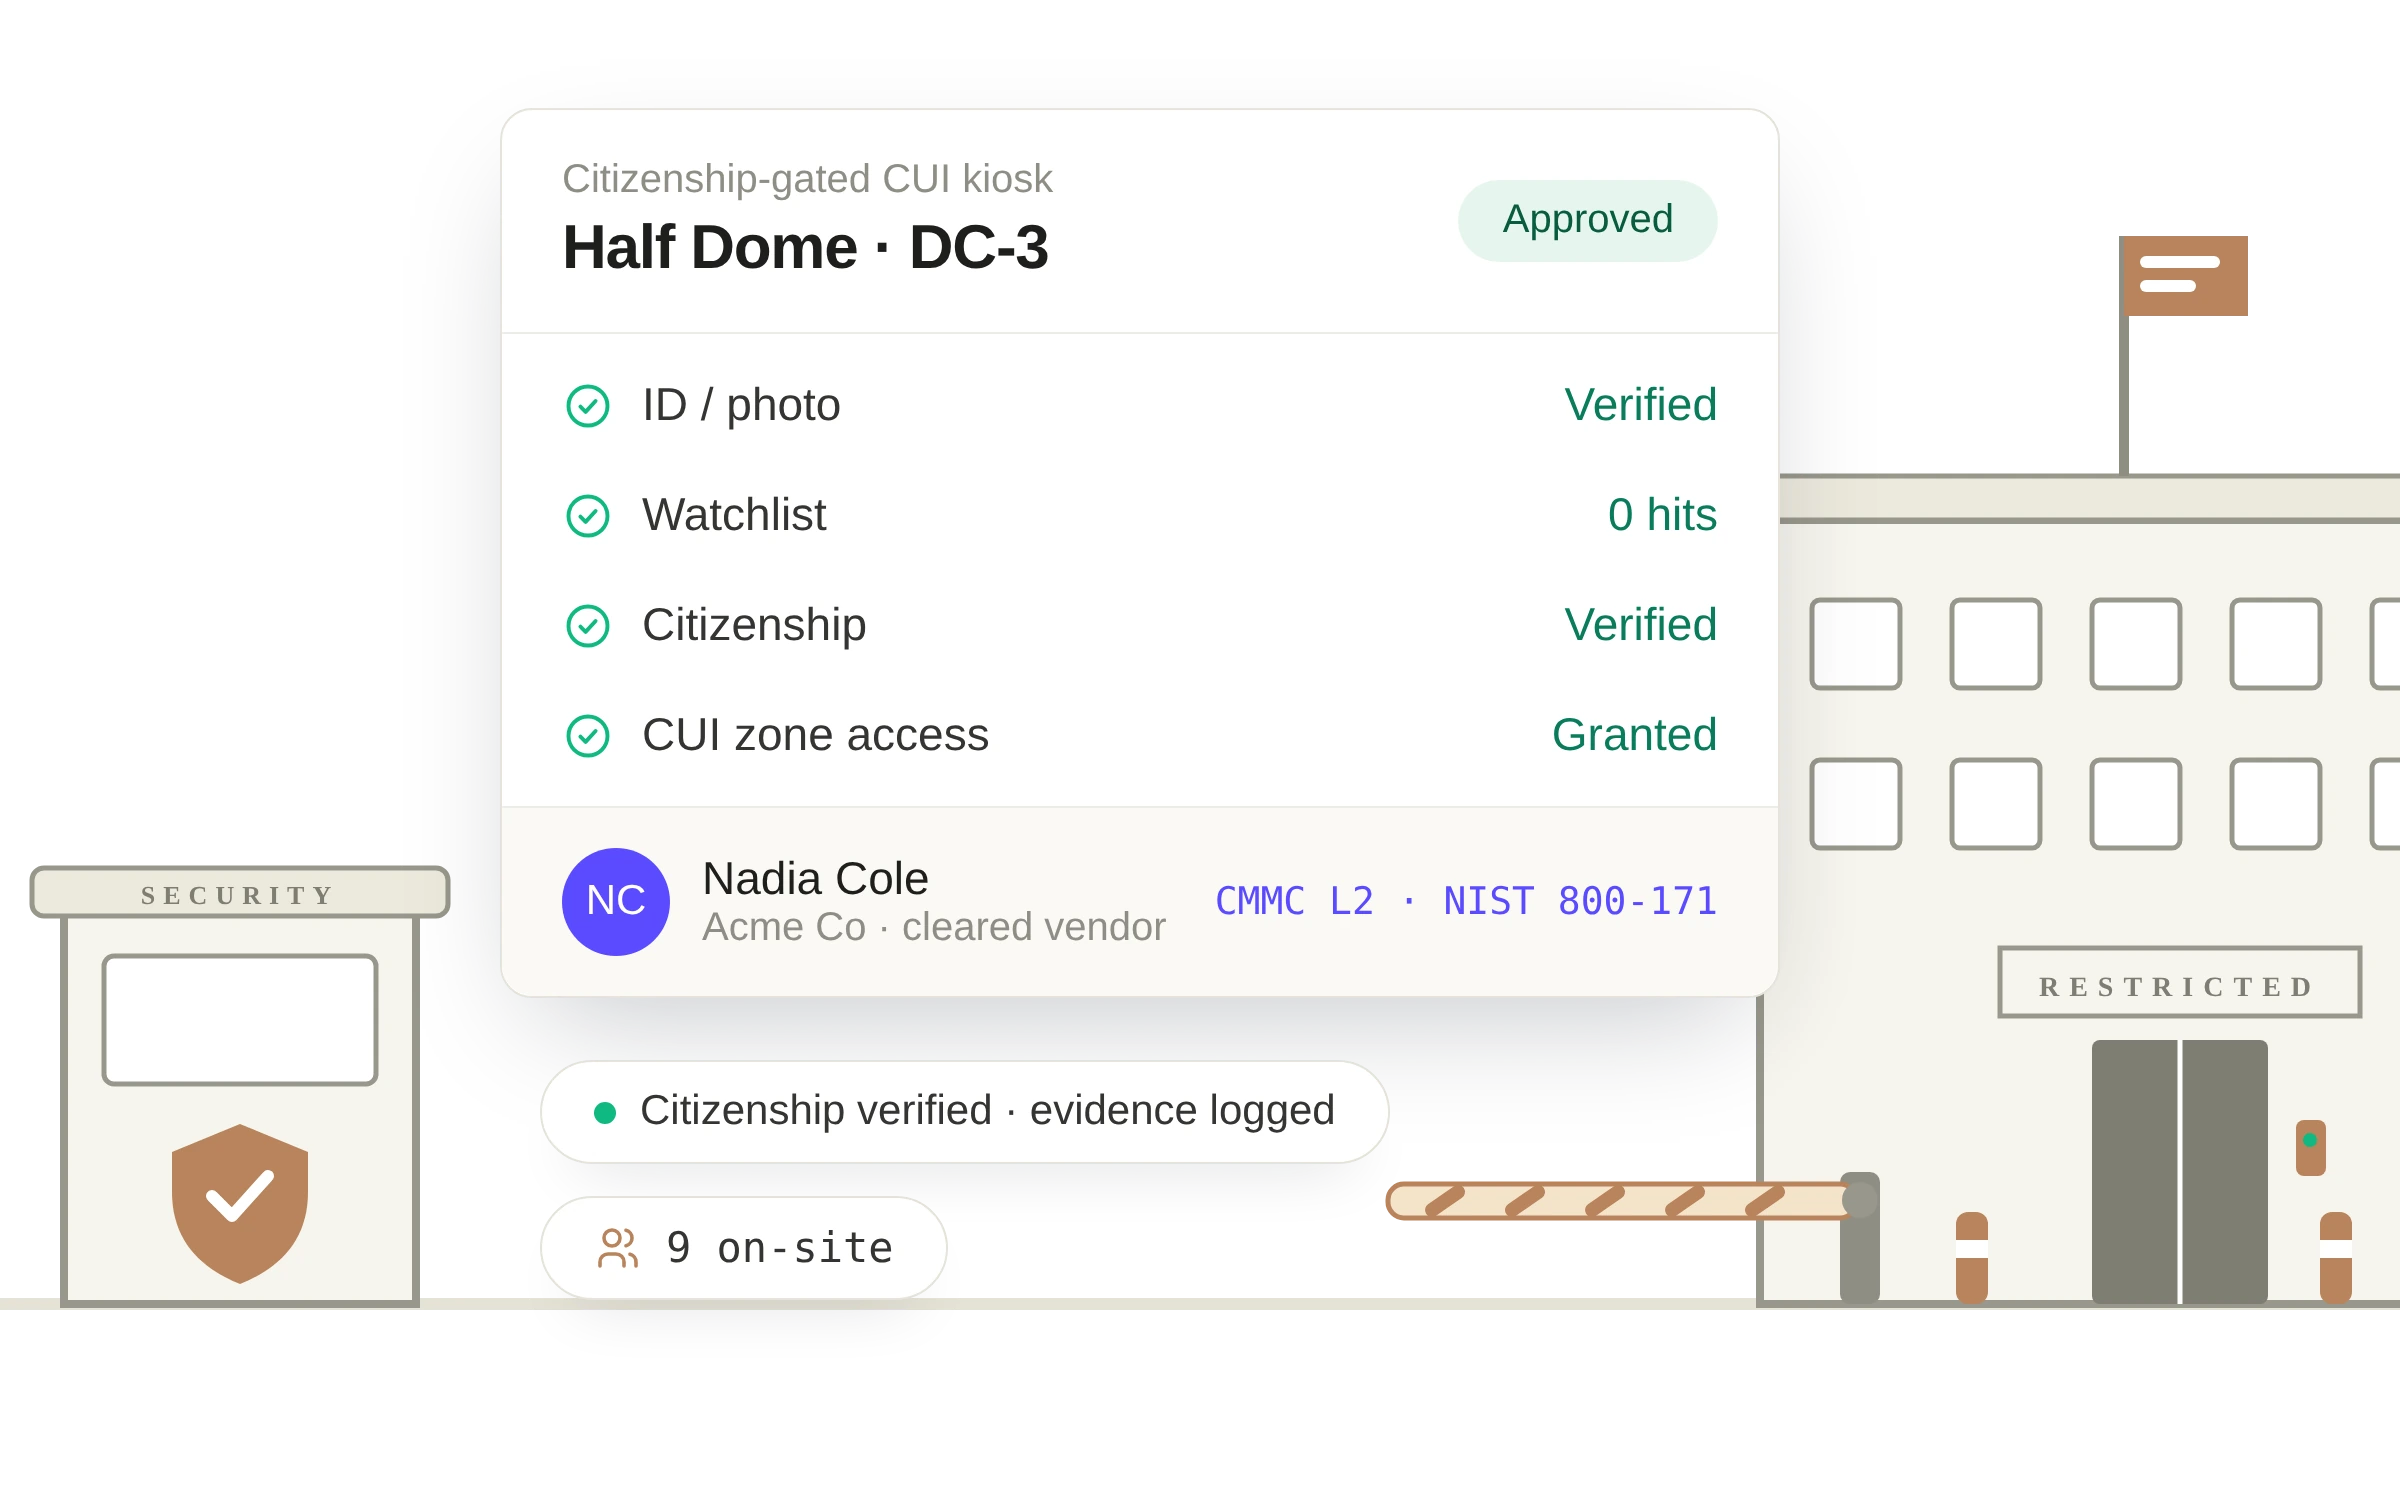
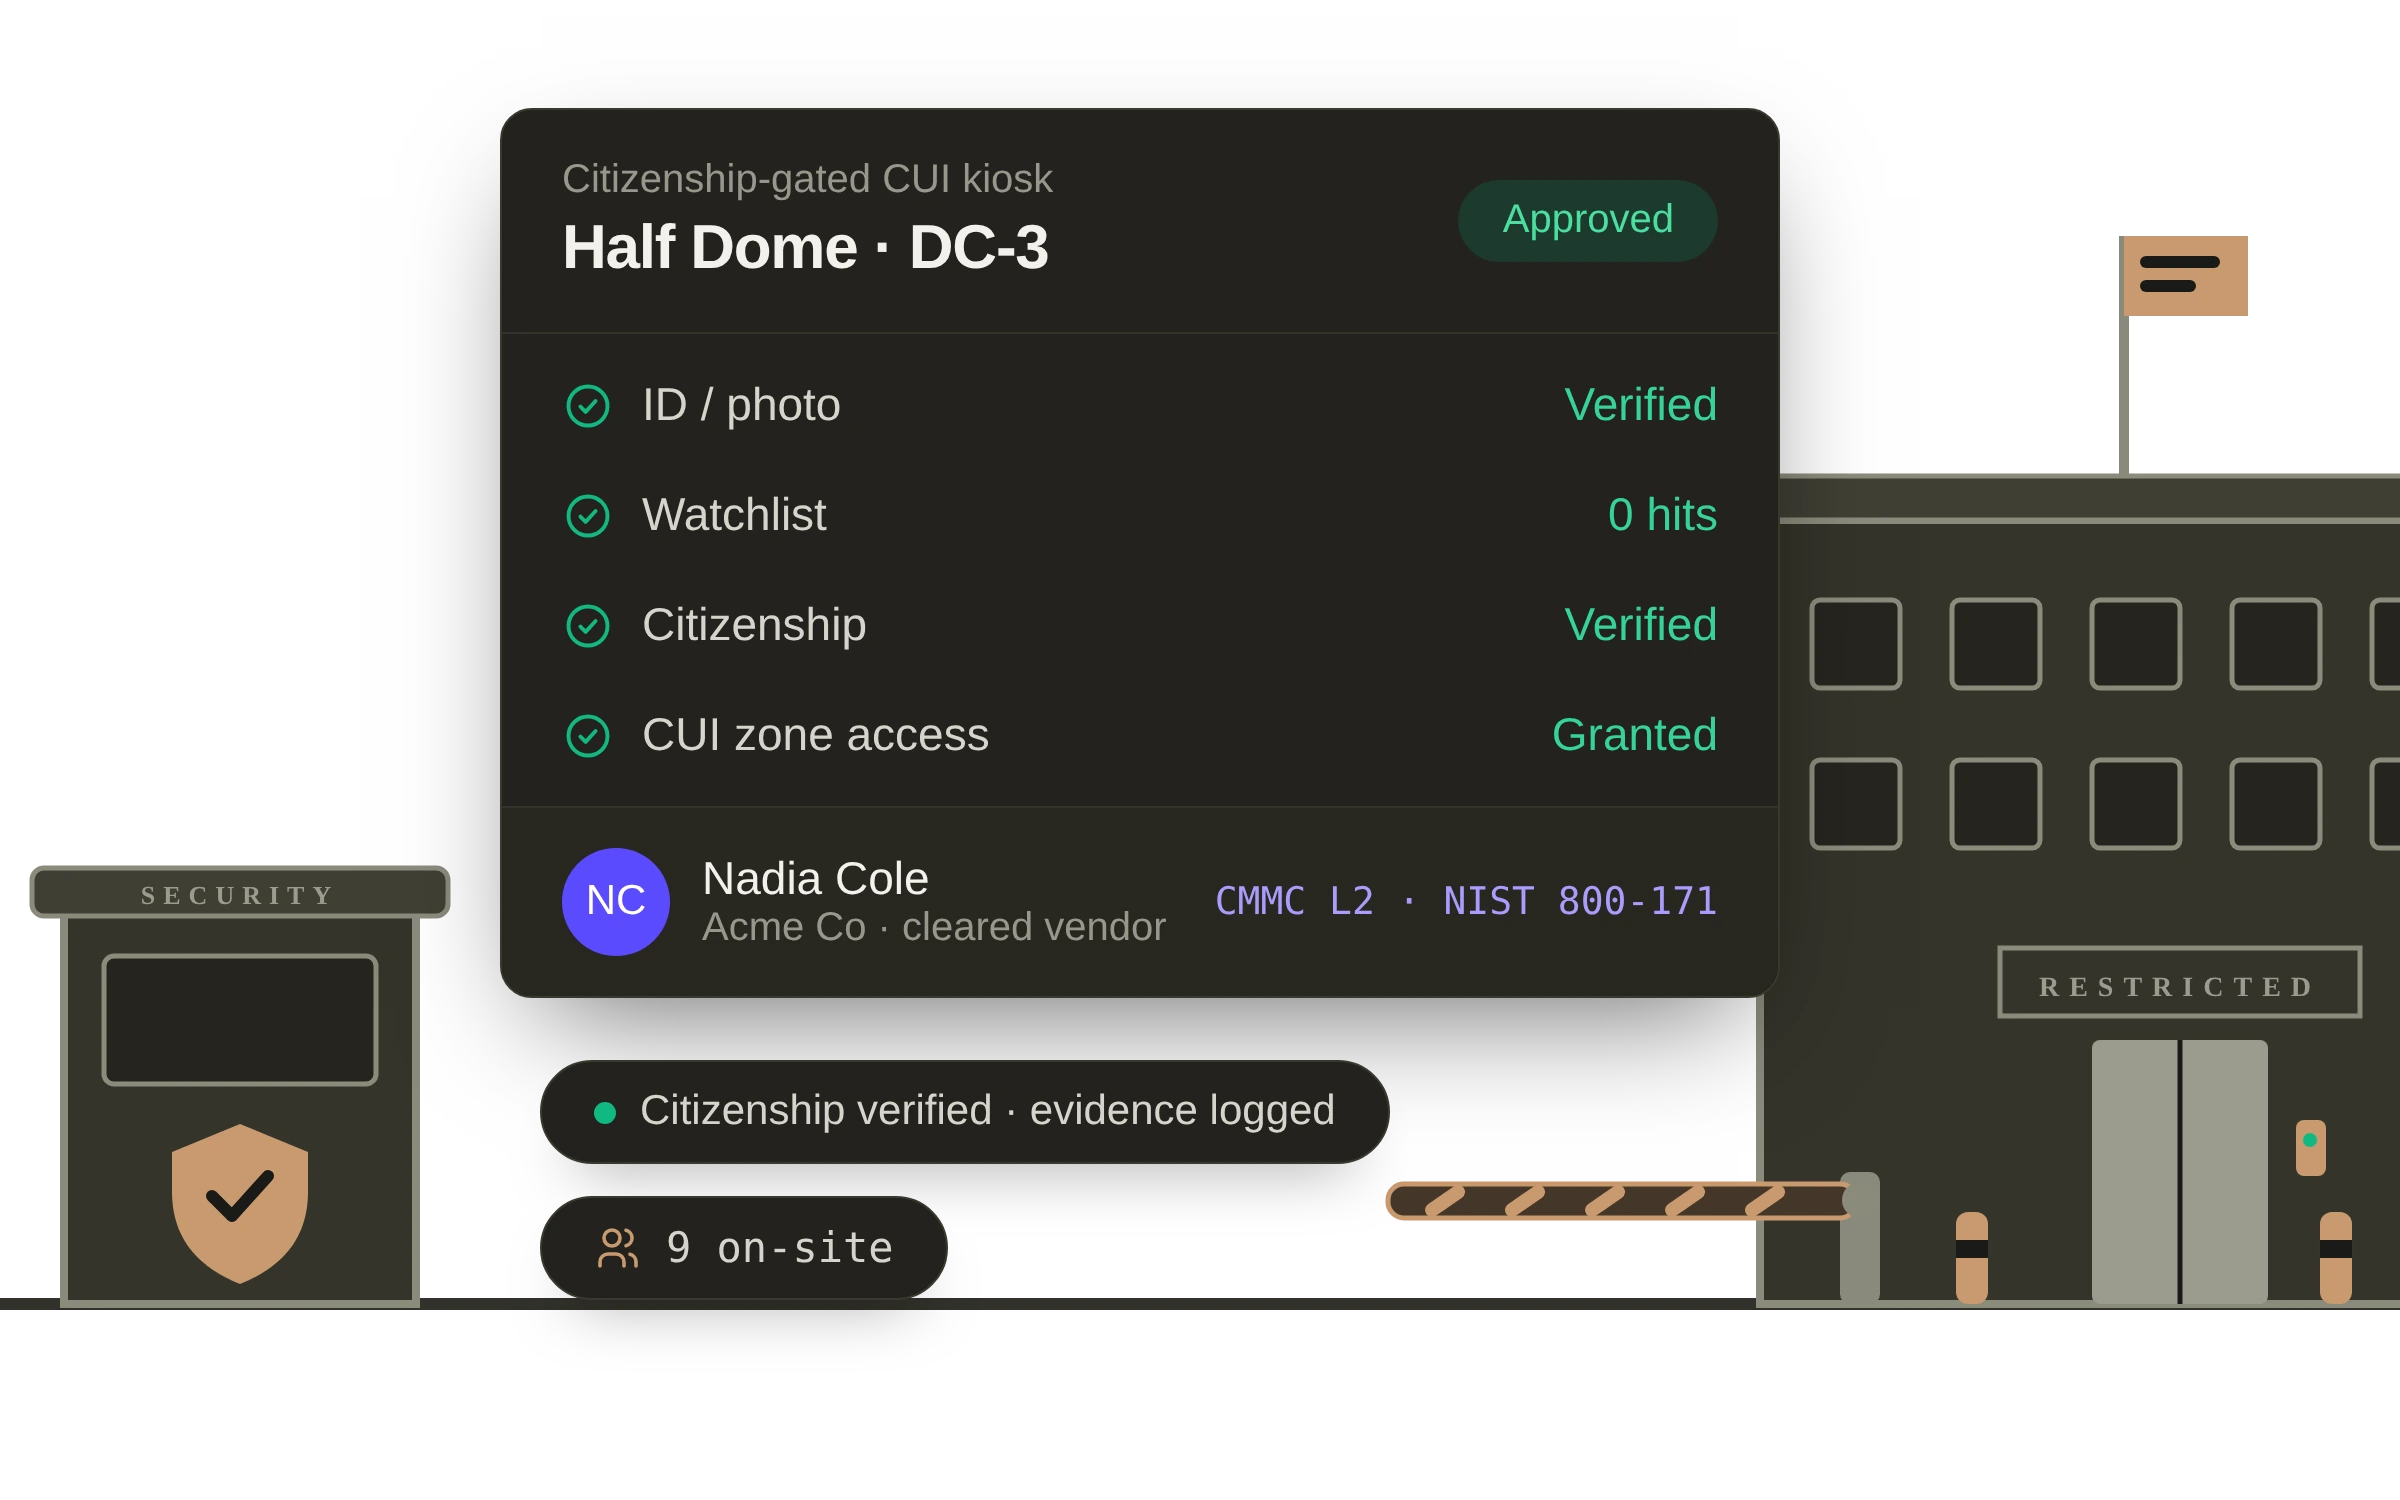
Whatever happens to the CMMC timeline, PE.L1-B.1.IX doesn't change: escort visitors, monitor their activity and keep a log of physical access. Visitly keeps that record at every site, with the citizenship gating and denied-party screening your ITAR and EAR program relies on, and little work from your team. When your assessor asks, you export the answer.
Visitly holds SOC 2 Type II and ISO 27001 certifications · 1,300+ organizations across 40+ countries
Escort visitors. Monitor them. Keep the physical access log.
Export the answer when your assessor asks.
Running an ITAR or EAR program too? The same visitor record supports it.
Citizenship is checked at the kiosk, and each ITAR- or EAR-controlled area is allowed or blocked by nationality. Foreign nationals go through the escort workflow, and every escort is time-stamped. Denied-Party Screening checks each visitor against government restricted-party lists through the Visual Compliance (Descartes) integration. Signed NDAs and ITAR acknowledgments stay with the visit record. Your team can search and export the log by site and date for the ITAR or EAR file.
The whole visitor compliance stack, on one platform.
Small suppliers carry the same flow-down obligations as their primes. Visitly puts every visitor control your program needs in one platform, with one set of records for the assessor.
Other vendors sell these controls as top-tier upgrades or add-ons. On Envoy, ID scanning, blocklists and restricted-party screening all need the Enterprise plan, which has no published price. Visitly is priced per location, never per visitor or per employee, and our per-location pricing is published.
Your gate runs it from day one. Your team doesn't staff a project.
Visitors check themselves in, in under 15 seconds. Your gate sees photo, ID, watchlist and citizenship results in one view and handles only the exceptions. Contractor crews are pre-registered in bulk, up to 200 per event. A basic setup takes under an hour, integrations such as SSO, SCIM, access control and HRIS take a couple of days, and multi-site rollouts take one week to one month. Switch Assist handles the migration from your current system. SentinelOne moved off Envoy and went live across 7 sites in under a week.
Comparing Envoy for CMMC, ITAR and EAR? Look at what sits behind its Enterprise plan.
Envoy is a workplace platform, and it markets ITAR, EAR and CMMC support. Its ID scanning, blocklists and restricted-party screening are all Enterprise-only, at a custom price. Visitly is visitor compliance first: area-level citizenship gating, a NIST 800-171 mapping and GCC High, on one platform.
Visitly vs Envoy
CMMC visitor management: common questions
What is a CMMC visitor management system?
A visitor management system that keeps the visitor-side records a CMMC program needs: who visited, who they saw, who escorted them, what they signed and when they left. Visitly captures photo, ID and signed acknowledgments at check-in and keeps every entry in an immutable audit log, with search and export built in.
Does Visitly make us CMMC compliant?
No. Your organization owns its CMMC program, and the C3PAO assesses it. Visitly supplies the visitor-side records, controls and evidence exports that support the program, plus a NIST 800-171 Rev 2 control-mapping reference under NDA. Visitly does not certify, attest or guarantee your compliance with any framework.
Does the CMMC timeline change what we need for visitors?
No. Escorting visitors, monitoring their activity and keeping audit logs of physical access is a Level 1 practice (PE.L1-B.1.IX), so it applies whatever happens to Level 2 certification dates.
What does Visitly cost a small defense contractor?
Visitly is priced per location, not per visitor or per employee, and our per-location pricing is published at visitly.io/pricing. ID verification, watchlist screening, citizenship gating, escorts and audit export all run on one platform, and denied-party screening connects through the Visual Compliance (Descartes) integration. Tell us how many sites you run and what your program needs, and we'll send your price.
How do you handle foreign nationals, escorts and export-controlled areas?
Visitly checks citizenship at the kiosk and allows or blocks each regulated area by nationality, for ITAR- and EAR-controlled areas alike. Visitors who need an escort go through the escort workflow, and every escort is time-stamped. Denied-Party Screening against government restricted-party lists runs through the Visual Compliance (Descartes) integration, and signed NDAs and ITAR acknowledgments are kept with the visit.
How long does it take to deploy?
A basic setup takes under an hour. Integrations such as SSO, SCIM, access control and HRIS take a couple of days, and a multi-site rollout takes from one week to one month, depending on how ready your team is. Switch Assist handles the migration from your current system.
Does Visitly work with our access control, identity systems and GCC High tenant?
Yes. Visitly connects to Genetec Security Center, LenelS2 NetBox, C•CURE 9000, Brivo and Kisi for access control, and streams events to your SIEM. SSO works through Okta, Entra ID, ADFS or any SAML 2.0 identity provider. For Microsoft GCC High tenants, Visitly integrates with Entra ID for SSO and directory sync, with Teams for host alerts, and with OneDrive for signed documents.
Is Visitly FedRAMP authorized?
Visitly is not FedRAMP authorized. We hold SOC 2 Type II and ISO 27001 certifications, host on AWS with US region pinning, and serve state, county and transit-authority customers. If FedRAMP is a hard requirement for your procurement, we'll say so plainly and look at your requirements together.
Start with 1–5 sites. Roll out to every site.
One watchlist and a live record of who is on site, the same at every location. Pilot a few sites with a defined end date, then decide how to scale.
Send this to your IT team